Straight from the Huntress SOC, no sales pitch. ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏  ͏ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­ ­  


20260713_EmailHeader_LeftAligned_LTMode_600x118

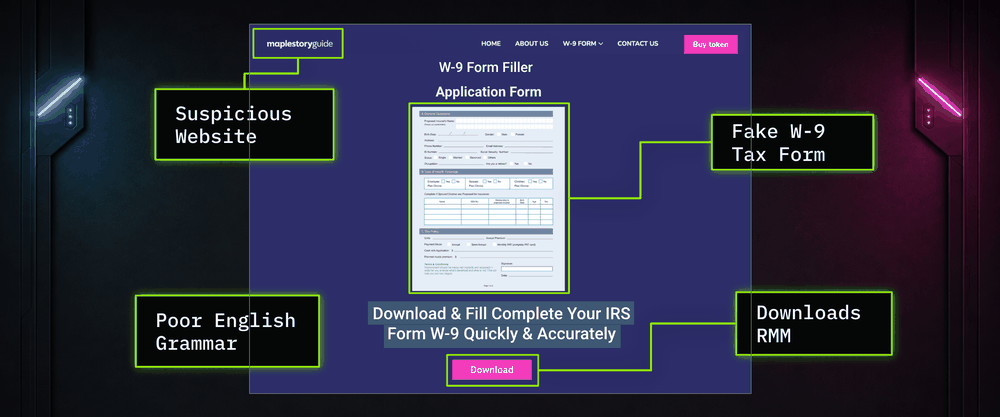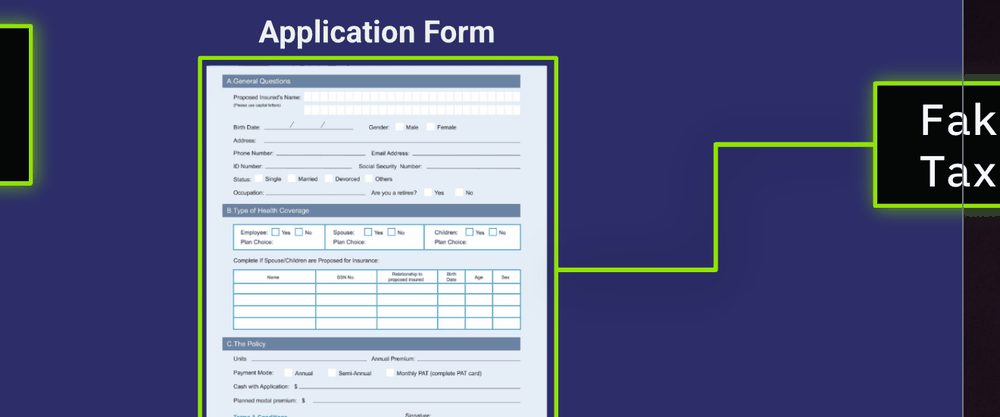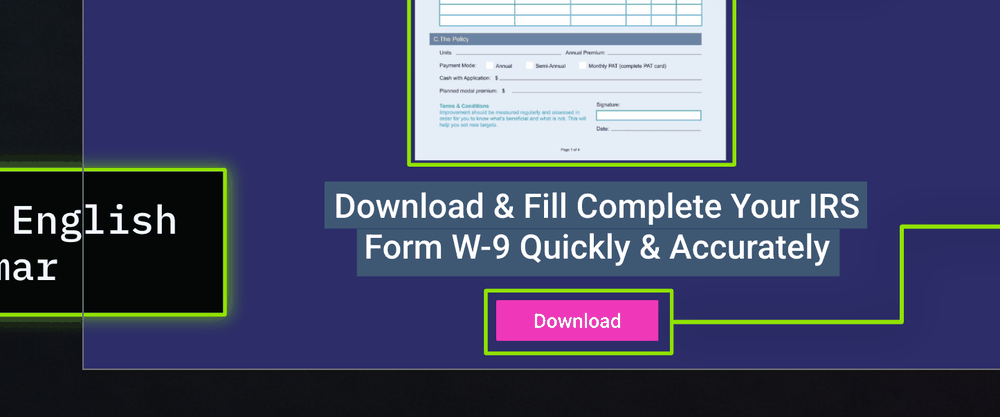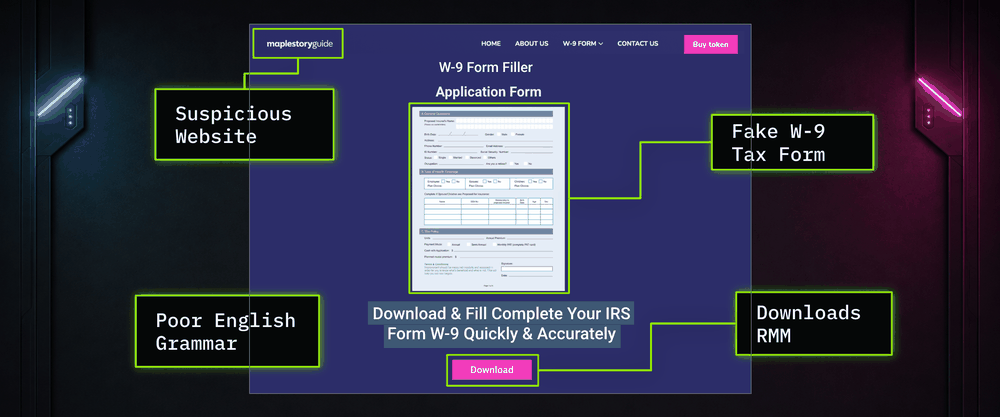
Have you ever downloaded a tax form? One user thought they were doing exactly that, but unfortunately, they were on a malicious site.

RMM installer tax form example

What they actually got was a fake RMM installer. That’s a standard IT tool that attackers love to abuse to gain control over their victims’ devices.


Thankfully, the Huntress SOC caught the malicious RMM because it was running from the downloads folder. In the process, we discovered four other devices across our customer base that had downloaded the same file. 


This is nothing new. Attackers have been leaning hard on the remote tools your team already trusts instead of writing new malware. Here's the pattern, straight from our SOC:

20260817_RMMAbuse_eBook_LPGraphic

RMM Abuse: Your Trusted IT Tools Are Now Hackers' Favorite Weapon →

RMM abuse isn't the only attack path we're watching:

  • A vendor payment email that was actually a $100,000 BEC attempt. It looked routine, right down to the account details. A Huntress employee followed procedure and picked up the phone before wiring anything.

  • A fake Claude Desktop ad that ended in a RAT. Someone searching for a legitimate AI tool clicked a malicious ad instead. The install that followed dropped a fully functional remote access trojan.

  • Suspected DPRK IT workers hiding inside partner organizations. Not malware, not a phishing link. A fraudulent employee, hired and onboarded like anyone else, quietly funneling a paycheck back to a sanctioned regime.

  • A ransomware affiliate that rebooted into Safe Mode to kill EDR, and broke their own attack doing it. Safe Mode disabled our agent the way they wanted. It also disabled the malware they needed to encrypt anything.

Four different playbooks, all counting on a tool or a login you already trust.

– Jamie Levy

P.S. Prefer video to reading? Tradecraft Tuesday is our monthly livestream that walks through real attacker behavior our team is seeing out in the wild.

20260713_EmailFooter_TopLine_LTMode_600x4
Book Demo Start Trial Read Latest Live Events
20260713_EmailFooter_BottomLine_LTMode_600x33
LinkedIn Logo X Logo YouTube Logo Instagram Logo G2 Logo

Unsubscribe | Manage Preferences


Huntress Labs Inc., 6996 Columbia Gateway Drive, Ste. 101, Columbia, MD,21046 USA 833-HUNT-NOW


© 2026 Huntress. All Rights Reserved.