We've been heads-down supporting our customers in adopting agentic workflows for finding and fixing vulnerabilities. Since August, Wingman went from 5,000 fixes to more than 30,000. We got approved by both frontier labs for trusted cyber access. And we have exciting results to share! When the agent does the finding and the fixing, time to fix collapses from weeks to minutes.
Here's what's new...
The Data
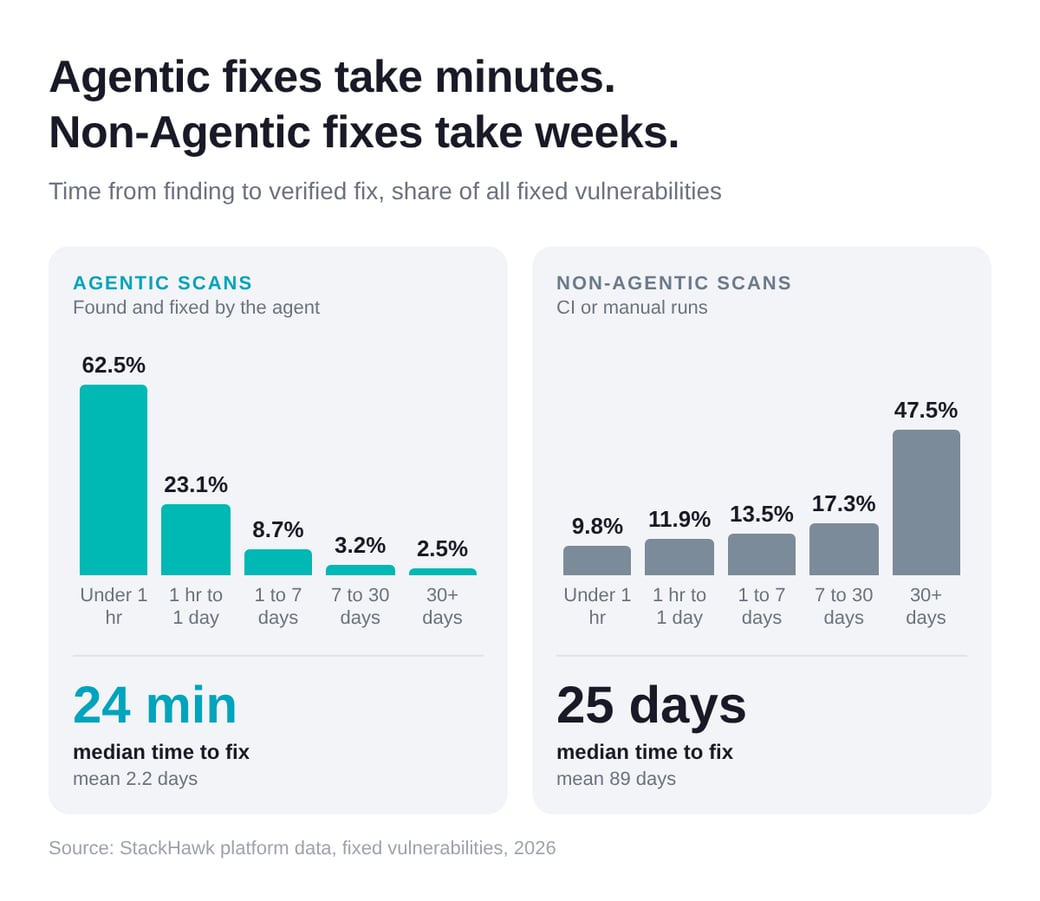
24 minutes vs. 25 days
We looked at every vulnerability fixed on the StackHawk platform this year and split them by how they were found. When a CI job or a manual run finds the vulnerability, the median fix takes 25 days. Nearly half sit open for more than a month. That is the ticket getting filed, triaged, prioritized, assigned, and eventually picked up by someone who has to reload all the context.
When the agent finds it, the median fix takes 24 minutes. 62.5% close in under an hour. The developer never leaves the coding session. The context is already loaded. The fix gets written, rescanned, and verified before anyone opens a ticket.
The lesson is not that agents write better patches. It is that the fix happens where the context lives. Move the finding into the agent loop and the backlog stops forming in the first place.
Live Training · Wednesdays, 10am MT
See the 24-minute loop on your own app
Bring a running app. In under an hour the StackHawk team will walk you through installing the skills, scanning with a single prompt, fixing a real finding with your coding agent, and verifying it closed. You leave with fewer vulnerabilities than you came in with.
Approved by Anthropic and OpenAI for trusted cyber access
StackHawk is now in Anthropic's Cyber Verification Program and OpenAI's Daybreak, their Trusted Access for Cyber program. Both labs vet who you are and what you intend to do, then keep watching after approval.
The reasoning that helps an attacker understand an exploit is the same reasoning a defender needs to fix it. These programs let our research and engineering team use frontier models on the defensive work their safeguards would otherwise block: validating findings, testing fixes against real attack paths, and checking remediation logic before it ships.
Insisting on a human approving every step of an agent's work is hurting security's ability to keep up with engineering. StackHawk CEO and Co-Founder, Joni Klippert, and Joe Sullivan make the case for a different control: let the agent investigate, fix, and test inside limits that security and engineering set together, then put a human on the final review and the release decision.
A record of who clicked approve does not establish what they understood. You can delegate the work without delegating the responsibility.
Asked why so many organizations can't identify and contain incidents, Joni's answer: "the answer is math." Roughly 100 engineers for every security professional, and the window from discovery to exploit is now negative.
"Finding was never the hard part." Duncan Riley on how Wingman runs when the agent marks a feature complete, patches what it finds, and rescans before the PR opens.